Cybersecurity Leadership.Built for Execution.
VULNSEE is a global cybersecurity advisory and security services company headquartered in Jerusalem, working with organizations in Europe, the US, the UK and Israel, helping executives, boards and regulated organizations turn complex risk into clear decisions and accountable action. From strategy and governance to testing, implementation and resilience, our multidisciplinary teams work across the full security lifecycle.
When security programs stop making sense
Most organizations have security tools, some have a team. Fewer have a coherent program that connects posture to risk to business decision making. The result is a recurring pattern: audit findings that stay open, boards asking questions no one can answer, compliance obligations that never fully close.
VULNSEE was built to address that gap. We work with CISOs, boards, DPOs, and technology leaders to translate what their security environment actually means, and turn that understanding into specific, actionable, documented outputs.
We are headquartered in Jerusalem, working with organizations in Europe, the US, the UK and Israel. We support regulated entities, technology companies, and international enterprises across strategy, governance, and technical execution.
Leadership With Perspective.Delivery With Depth.
Executive judgment, multidisciplinary expertise and accountable execution. Working as one.
At VULNSEE, we bring together experienced professionals across cyber strategy, privacy, GRC, offensive security, cloud security and implementation. Each engagement is shaped around the organization’s actual exposure, business priorities and regulatory environment.
Our CEO and owner, Itzik Ramati, brings more than a decade of experience spanning cybercrime investigations at Lahav 433, enterprise cybersecurity leadership and regulated industries. As a technology entrepreneur and investor active across high tech and cybersecurity, he brings a broader business perspective to every engagement by connecting technical reality with commercial priorities, bringing in the right specialists and ensuring that decisions carry through to execution.
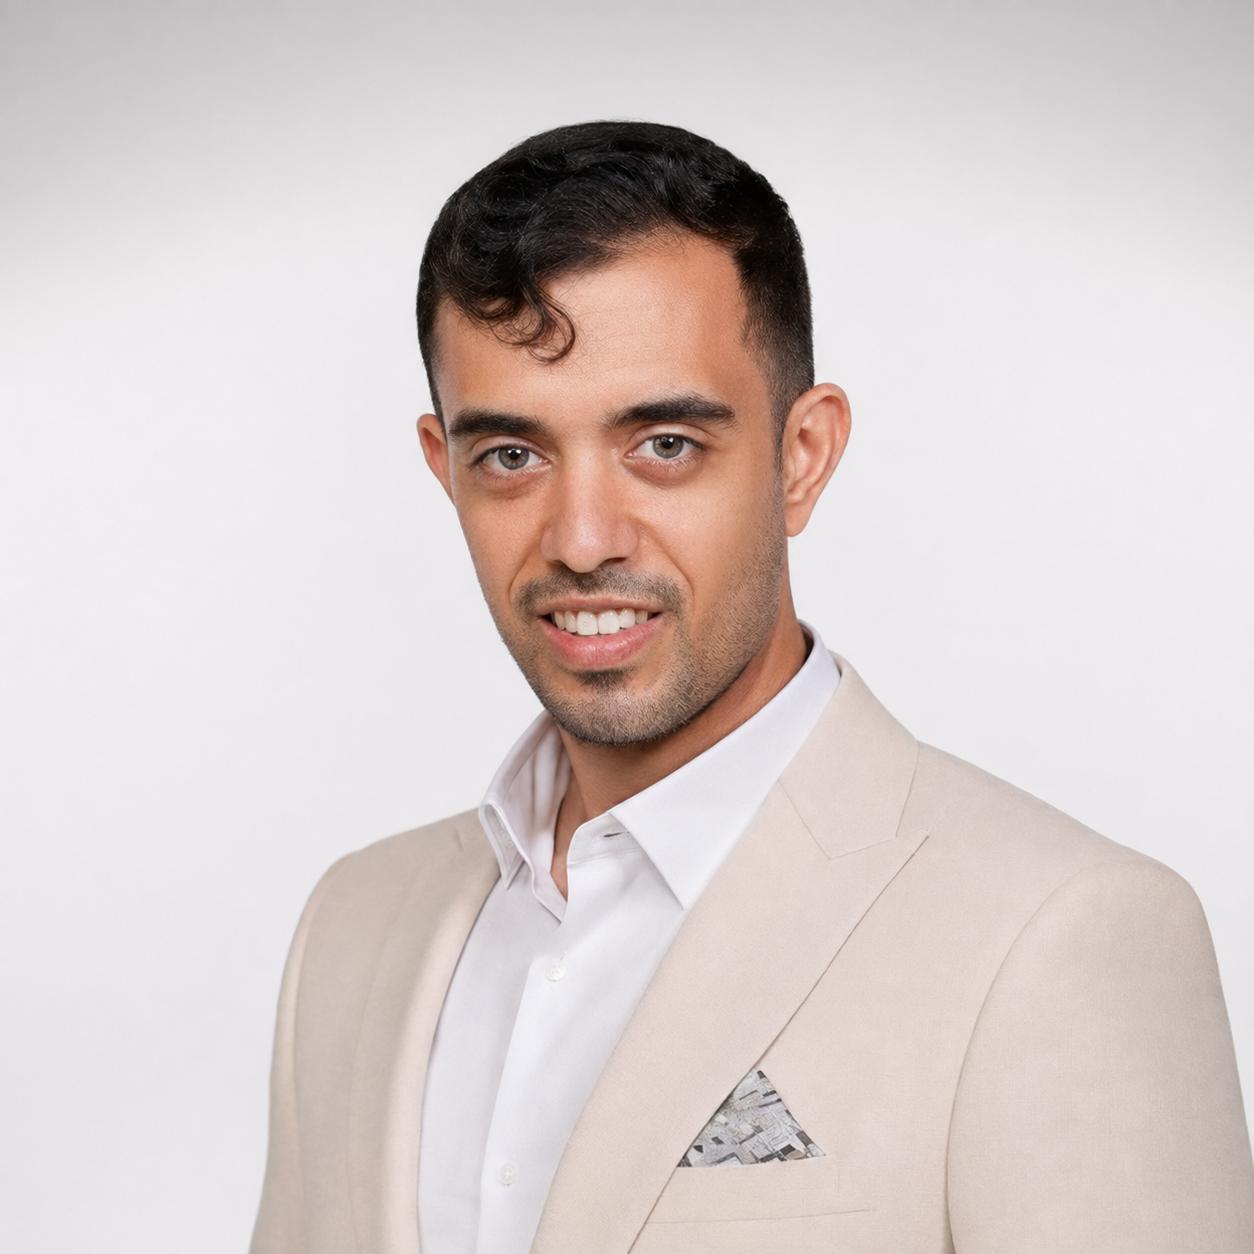
Itzik Ramati
We translate cyber risk, regulatory exposure and technical reality into clear business priorities.
We bring together the right professionals across strategy, privacy, GRC, offensive security, cloud and implementation.
We maintain clear ownership and carry decisions through from assessment to execution.
The standards we hold ourselves to
Independent by Design
Our recommendations are not dictated by a single vendor, platform or generic framework. We evaluate each organization in context and recommend the actions, controls and priorities that best support its actual risk, regulatory obligations and business objectives.
Clarity before coverage
A hundred page report that no one acts on is not a deliverable. We measure outputs by whether they produce decisions, not by volume.
Scope that fits the organization
Generic frameworks miss context. Risk treatment for a regulated financial firm looks different from a SaaS startup. We scope to the environment, not the template.
Auditable documentation
Every recommendation is backed by evidence a regulator, insurer, or board can review. If it cannot be substantiated, it does not go in the report.
Direct delivery and execution
Advisory ends when the work is complete and the organization knows what to do with it. We stay with engagements through to actionable outputs.
"We believe complex security challenges require capable teams and diverse perspectives. We are committed to supporting professional excellence, inclusive leadership and greater representation of women across cybersecurity within our organization and across the industry."
Who we work with
Our team works across fintech, financial services, healthcare, enterprise groups, defense supply chains, SaaS and industrial IT/OT environments, adapting each engagement to the sector’s operational and regulatory reality.
Boards & Executive Teams
Governance level questions about cyber risk, regulatory exposure, and what the organization's current security posture means for decision making.
CISOs & Security Leaders
External advisory, program validation, and specialist support for security leaders who need an independent perspective or additional capacity.
DPOs & Privacy Teams
Organizations managing GDPR, CCPA, Israel's Privacy Protection Law, or multiple overlapping privacy obligations across complex data environments.
Regulated & Technology Companies
Financial services, healthcare adjacent, defense supply chain, SaaS, and organizations with contractual or regulatory security obligations.
What we deliver
Global Expertise.
Locally Rooted.
VULNSEE is based in Jerusalem, operating at the intersection of Israel's unique regulatory environment and global security standards. We provide organizations with the working fluency needed to navigate complex local requirements while maintaining international market obligations.
Our expertise bridges the gap between:
Israeli Regulation: Deep navigation of the Privacy Protection Authority, National Cyber Directorate, MALMAB (defense supply chain), and sector specific directives from the Bank of Israel and Ministry of Health.
Global Frameworks: Clear alignment with GDPR, CCPA, ISO 27001, NIST CSF, SOC 2, and PCI DSS for cross border data flows and international expansion.
We address the complete regulatory picture rather than an isolated checkbox or regulator. We help organizations harmonize these diverse requirements into a single, high standard security posture that enables global growth without compromising local compliance.
- Privacy Protection Authority
- National Cyber Directorate
- MALMAB / defense supply chain
- Bank of Israel, Ministry of Health
- GDPR, CCPA
- ISO 27001, NIST CSF, SOC 2, PCI DSS
Need clarity on your cyber, privacy, or compliance posture?
We work with boards, CISOs, and compliance teams to define exposure, prioritize action, and build security programs that hold up to scrutiny.
